NextDNS breaks when using DNSSEC with Asus Router
Hello,
Since last night it seems that NextDNS breaks when enabling DNSSEC support on ASUS router.
Model: TUF-AX3000 V2 (gnuton merlin build)
Config:
- Enable DNSSEC support: Yes
- Validate unsigned DNSSEC replies: Yes
Disabling DNSSEC support seems to do the trick.
I had these router and NextDNS (security settings, privacy lists, etc) configs for months and there was no problem. There was no software update on the router. Suddenly, it no longer works.
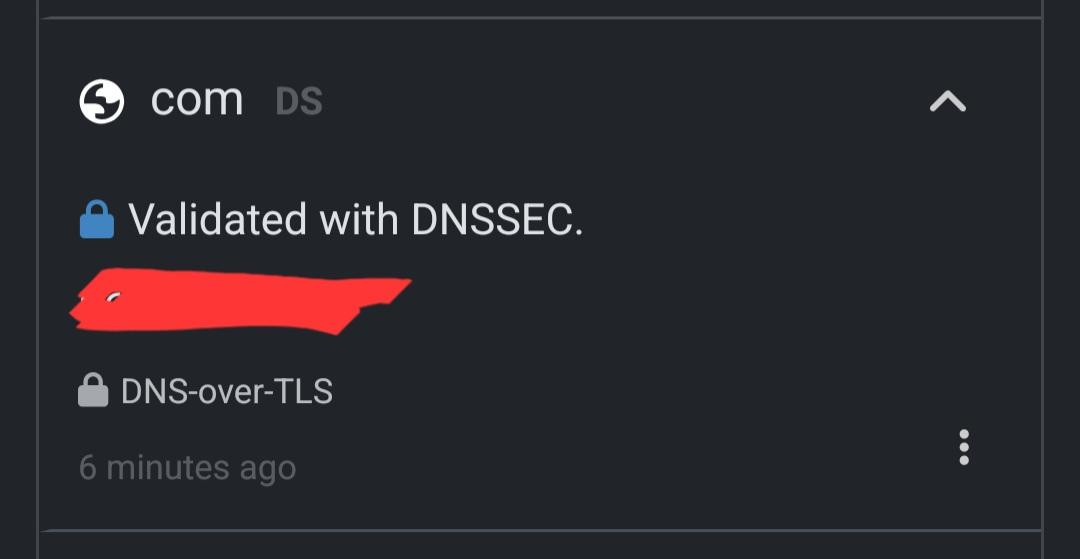
The only weird thing that I noticed is that now there are a ton of these entries in Analytics:
Has anyone else noticed a similar issue recently?
10 replies
-
I’m experiencing exactly the same issue after updating my ASUS router. In my case, it’s an ASUS RT-BE92U.
As a workaround, I manually configured the NextDNS IP addresses under LAN > DHCP Server and set “Advertise router’s IP in addition to user-specified DNS” to No.
This seems to have resolved the issue for me. Of course, the downside of this workaround is that DNS traffic is no longer encrypted.
Hopefully this helps someone else experiencing the same problem.
-
I'm experiencing what appears to be the exact same issue with NextDNS and DNSSEC on my ASUS ZenWiFi BQ16 Pro running stock firmware 3.0.0.6.102_39256.
This morning, multiple devices on my network were unable to load certain websites, even though general Internet connectivity was working.
I investigated and found:
DNSSEC enabled:
nextdns.ioreturnedSERVFAILthrough both the router's IPv4 and IPv6 DNS interfaces.Cloudflare comparison: Querying
1.1.1.1directly returnedNOERRORand the correct IP addresses.Other domains:
google.comcontinued resolving normally through the ASUS router.NextDNS logs: An enormous increase in DNSSEC DS queries, particularly for
com, matching your screenshot. I recorded 9,882comqueries over a two-hour period.DNS configuration: NextDNS over DNS-over-TLS (DoT), Opportunistic mode, with ASUS DNSSEC support enabled.
At approximately 11:35 AM EDT today (October 12), I disabled ASUS DNSSEC support without changing my NextDNS DoT configuration.
The results were immediate:
nextdns.iobegan resolving normally through both IPv4 and IPv6.The abnormal DNSSEC DS-query traffic stopped completely in the subsequent observation window.
Overall DNS query volume dropped approximately 86%, from 294 queries/minute to 40 queries/minute.
My router's logs show that changing the DNSSEC setting also restarted
dnsmasqandstubby, so I can't completely rule out the service restart as a contributing factor.However, the similarity between our symptoms, particularly the sudden appearance of excessive
comDS queries, is striking.Since we're using different ASUS hardware and firmware, and neither configuration had previously exhibited this behavior, I suspect a recent upstream DNSSEC-related change may have exposed an interoperability problem.
For now, I've left ASUS DNSSEC disabled while continuing to use NextDNS over DoT.
Hopefully NextDNS can investigate whether something changed recently in its DNSSEC handling or upstream infrastructure.
-
You nailed it. Exact same issue on my RT-AX58U running firmware 3.0.0.4.388_25277. As soon as I disabled DNSSEC, lookups started working again. This workaround is not a desirable long term solution, so I hope someone from the NextDNS team will read this thread and implement a fix.
-
This also broke our internet connection. NextDNS internet works, Cloudflare DNS-over-TLS works, but if I try to use NextDNS for this I get DNS_PROBE_FINISHED_BAD_CONFIG. Nothing had changed locally.
-
Guys, I just found this, you might wanna check it out:
https://github.com/gnuton/asuswrt-merlin.ng/issues/1026
I don't know if that is the root cause for what we have here, but considering when the bug on github was raised, it doesn't seem to be a coincidence -
this has broken usage of iPads and LGTV on my network.
removing DNSSEC on my Asus router also fixed it. -
Update: Could this be related to the DNSSEC root key rollover on October 11?
I noticed the timing lines up almost perfectly with the DNSSEC root KSK rollover that happened yesterday.
Cloudflare wrote about it here:
https://blog.cloudflare.com/root-ksk-2024-rollover/Apparently, resolvers that haven't properly updated their trusted root key can start returning
SERVFAILafter the rollover.That would explain why multiple ASUS routers suddenly started having issues without any firmware changes.
On my BQ16 Pro, disabling DNSSEC immediately restored resolution, and the flood of
comDS queries stopped. Overall DNS traffic dropped about 86%.I'm wondering if the rollover exposed a bug in ASUS's DNSSEC handling rather than an issue with NextDNS itself.
Has anyone from NextDNS looked into whether the rollover could be responsible?
-
does NextDNS monitor these posts?
Content aside
-
5
Votes
- 3 hrs agoLast active
- 10Replies
- 293Views
-
7
Following